18027 stories
·
175 followers

Warner Bros. drops final trailer for Dune: Part Three

1 Share

The end of the year is fast approaching and with it, the pre-Christmas release of Dune: Part Three, the final installment in Denis Villeneuve's acclaimed adaptation of sci-fi author Frank Herbert's novel(s). Warner Bros. gave us a broody and haunting extended teaser in March and a July trailer jam-packed with tantalizing hints of what to expect, along with plenty of Easter eggs to delight avid book fans. Now we've got one last action-packed trailer setting up the final act for iconic anti-hero Paul Atreides (Timothée Chalamet).

(Spoilers for first two films in the franchise below.)

Previously, 2021’s Dune culminated in the brutal defeat of House Atreides by rival House Harkonnen, with Paul and his mother, Lady Jessica (Rebecca Ferguson), fleeing to the desert and taking refuge among the Fremen. Among them is Chani (Zendaya), whom Paul has been seeing in visions all along.

In Dune: Part Two (2024), Paul ingratiated himself with the Fremen, learned to ride a sandworm, and won Chani’s love. A pregnant Lady Jessica had her own plans for Paul as a messiah figure to fulfill a Bene Gesserit prophecy. Ultimately, Paul challenges the emperor, defeats his champion, and demands the Princess Irulan (Florence Pugh) as his wife. The other Great Houses reject Paul as ruler, so he launches a holy war against them. And Chani rides off on a sandworm after refusing to bow down to Paul.

Dune: Part Three draws on Herbert’s novel Dune: Messiah and will take place roughly 17 years after the end of Part Two, according to Villeneuve, as Paul faces the consequences of his earlier actions. Specifically, an assassination plot is brewing, and Chani is "involved." Per the official synopsis:

Dune: Part Three is set nearly two decades after Paul Atreides seized control of the Imperium. Now a ruthless Emperor, Paul must face the consequences of his reign as old allies return, terrifying new threats emerge, and betrayal lurks in every shadow. Haunted by visions of Imperial collapse and the reappearance of his long-lost love, Paul is drawn into a sweeping conspiracy, with Chani at the heart of its unfolding mystery. As enemies close in, Paul must confront the true cost of power and the fate of those he loves the most.

Chalamet is back as Paul Atreides, along with Zendaya, Pugh, and Ferguson. Josh Brolin reprises his role as weapons master Gurney Halleck; Javier Bardem is back as Stilgar, leader of the Fremen tribe at Sietch Tabr; and Jason Momoa returns as Duncan Idaho/Hayt. Joining the cast are Anya Taylor-Joy as Paul’s younger sister, Alia; Robert Pattinson as the villainous Scytale, who plots to dethrone Paul; Isaach de Bankolé as Paul’s former Fedaykin, Farok; Nakoa-Wolf Momoa (son of Jason) as Paul and Chani’s son, Leto II Atreides; and Ida Brooke as Paul and Chani’s daughter, Ghanima Atreides.

Dune: Part Three opens in theaters on December 18, 2026, going head to head with Avengers: Doomsday.

Read full article

Comments


Read the whole story
fxer
1 hour ago
reply
Bend, Oregon
Share this story
Delete

Code-execution flaw in UEFI firmware affects most servers on planet Earth

1 Share

Defenders across the world face the burden of responding to yet another botched code-execution vulnerability, this time in boot-time firmware used by most of the world’s server vendors and data centers.

The vulnerability, with a severity rating of 9.5 out of 10, resides in the TianoCore EDK II, an open source codebase that hardware makers and cloud providers use to create the UEFI firmware that runs during the boot-up sequence. Last year, a representative of the UEFI Forum called EDK2 the "preeminent solution / implementation of the UEFI specifications." Virtually all UEFI suppliers (sometimes still called IBVs or independent BIOS vendors), including AMI, Insyde, and Phoenix, use the reference code extensively. Project Mu, Microsoft's hardened EDK2 fork, used the code containing the vulnerable component as well.

The vulnerability, tracked as CVE-2026-97631, is a memory-corruption flaw in an ICMP component that attackers can exploit to execute malicious code that runs before the operating system and firmware can implement defenses like Secure Boot, which establishes a chain of trust for all code, including the Trusted Platform Module (TPM), loaded during boot. While final payloads delivered by CVE-2026-97631 have no persistence—meaning they run only once—they can give attackers a wide opening to install other payloads that also run each time early in the boot process.

The cat has left the bag

The parties that discovered CVE-2026-97631—Alex Matrosov of Anthropic and Dan Holmes of Google—had arranged for it to stay under wraps until a coordinated disclosure that was scheduled for January. AMI, a maker of motherboards and other hardware, published this pull request last month that detailed the vulnerability and included a code fix. Once the post came to the attention of the discovering parties, TianoCore Project members published a public advisory last week.

With publicly available patch code, it will be trivial for advanced hackers to learn how the vulnerability is triggered and to build working exploits. Further compounding the urgency, patching UEFI code vulnerabilities in millions of end devices sold and used by thousands of hardware makers and cloud providers is cumbersome and time-consuming. Word of the vulnerability comes six days after another botched disclosure, this one involving a critical code-execution vulnerability in the PHP programming language.

“This vulnerability in the ICMP parser of the EDK2 network stack is interesting in terms of how it affects the chain of trust and the broader ecosystem,” said HD Moore, creator of Metasploit and chief research officer at security firm Dragos. “An attacker intent on compromising a nearby endpoint or server could use this bug to hijack program flow at a point where the boot process still has access to sensitive components, like the endpoint's TPM. This could be used to break disk encryption for cases where an attacker has short-term network access (and it would be even easier in a theft scenario).”

CVE-2026-97631 is a 16-year-old buffer overflow in the PXE-Base Code driver (NetworkPkg/UefiPxeBcDxe), which is responsible for allowing servers, storage equipment, and other devices to boot using code downloaded from a local network. During this process—known as the pre-execution environment boot—the driver uses a network listener to monitor for ICMP errors. Because the driver doesn’t enforce a memory copy limit of 504 bytes, overwriting adjacent data, a malicious insider or a hacker who has gained low-level access to a local network can send an error message that appends code past this limit. The IUEFI module running on the CPU then becomes corrupted.

As the official advisory puts it:

During network boot, the PXE Base Code driver (NetworkPkg/UefiPxeBcDxe) keeps a receive request open for ICMP error messages and copies each received message into the fixed 504-byte field Mode.IcmpError of its private context structure. The copy loop's bounds handling is incorrect in both the IPv4 and IPv6 handlers (PxeBcIcmpErrorDpcHandle and PxeBcIcmp6ErrorDpcHandle): for a message longer than 504 bytes it still copies bytes into the field, and it advances the destination pointer by the cumulative rather than the per-fragment length, so an oversized message writes attacker-controlled bytes past the field. Nothing earlier on the receive path restricts the message length.

The malicious error can be delivered through a simple unicast sent from any network distance to a target device’s IP address, as long as it’s sent during the PXE boot sequence. An attacker can deliver a denial-of-service by causing the boot sequence to hang. When the attacker knows what the target firmware build is, it can plant a “counterfeit event” that executes the malicious code on the CPU in its UEFI firmware environment. The code runs in ring 0, a CPU's most privileged execution level. Because exploits bypass attestation processes designed to cryptographically prove to remote servers that the hardware is secure, they present a key opportunity for elevating limited privileges.

Yet another forever day

CVE-2026-97631 joins a long list of previously discovered vulnerabilities in UEFI or code that works closely with it. The most severe of them, LogoFail, stemmed from logo images included in the UEFI of just about every hardware maker. Rendering bugs allowed attackers to subvert the chain of trust UEFI enforces and go on to install malicious components before the OS loaded or Secure Boot ran. PixieFail was a vulnerability similar to CVE-2026-97631. It, too, was the result of faulty PXE boot flaws in EDK2. Following discovery of the vulnerability, researchers embarked on multiple fuzzing projects designed to surface other critical flaws in the open source code library. It appears those efforts failed to find this latest flaw.

Other recently discovered UEFI flaws include:

  • PKFail, a supply-chain failure resulting from non-production test platform keys, public for more than a decade before they were discovered, used in hundreds of device models
  • BootHole
  • Bootkit and
  • BlackLotus

Like CVE-2026-97631, exploitation or use of these payloads is appealing because it allows attackers to infect machines early in the boot process, before TPM and other defenses load, so they can inflict maximum damage. Given the ubiquity of CVE-2026-97631, Moore said it’s likely a "forever" bug that will live on in end-of-support systems.

There are important caveats and limitations to exploiting this latest vulnerability. As noted, some level of control over a local network is a prerequisite. That likely limits exploitation to insiders or attackers, such as nation-states or ransomware operators, who manage to gain low-level access inside a network and are looking for a way to elevate system rights. There’s no evidence yet that CVE-2026-97631 provides an initial entry point into a network. There are other hurdles to clear.

“For exploiting the vulnerability itself, an attacker needs to guess specific addresses within the target system, so it's not something that you can throw a single exploit at any target and get RCE across a diverse range of devices, but it needs to be tuned for each target model/version/configuration since the addresses will change based on those,” Jesse Michael, a principal researcher at firmware security firm Eclypsium, told Ars. “Unlike some of the previous, high-profile vulnerabilities like BootHole, Black Lotus, and Baton Drop, this vulnerability can be fixed with a basic code fix, which will require deploying a BIOS/UEFI update, but they don't need to deal with revocations, pk/kek/db/dbx key management updates, or making sure to update OS and provisioning media like you do with Secure Boot bypasses in the bootloader itself.”

CVE-2026-97631 doesn’t affect home and small office users, or any other users who boot their devices solely from disk drives. Instead, it applies only to organizations with machines that boot from local networks, or conceivably from Internet-connected resources. Even then, the targeted firmware must rely on EDK2, as opposed to a different reference implementation, and use the PXE functionality (which is turned on by default).

In an email, Intel said that none of its "commercial products currently under security support" are known to be affected. "Intel does not include the affected EDK2 functionality in its reference code, though it may be integrated by an OEM board vendor or system manufacturer," the company added. It advised customers to check with their system manufacturer for specific guidance. Publicly available Intel reference code, however, makes reference to EDK2. Further, TianoCore has said that each Intel-supplied UEFI development kit "is a fully validated implementation... for a specific revision of the EDK II source." Many other Intel documents reference EDK2 as well.

Arm, meanwhile, responded to a list of questions with: "CVE-2026-97631 is not directly applicable to Arm’s product portfolio." Like Intel, firmware the company makes available also borrows heavily from EDK2. TianoCore has also documented Arm's reliance on EDK2.

While it's possible some platforms are free of EDK2 code, it's prudent for users of all servers to investigate if CVE-2026-97631 affects them.

Questions sent to AMD, Phoenix Technologies, AMI, Microsoft, and Amazon—likely some of the other biggest organizations affected—went unanswered when this post went live. Without concrete answers to questions about the use of EDK2 by organizations like these, it’s impossible to say what or how devices are affected and what actions, if any, these organizations, or their users, should take. Representatives from the TianoCore Project also didn’t respond.

Some readers are likely to be unhappy at the lack of detail. Sometimes—particularly in cases involving botched disclosures that break embargoes months before they’re scheduled to lift—there’s no escaping the lack of actionable information in initial reporting.

Those affected should check with the maker of the firmware being used to boot their systems and ask for guidance. Beyond that, they should consider turning off network boot capabilities at least temporarily if possible. Firmware configurations should always enable security features such as TPM and Secure Boot whenever possible, although those defenses don't protect against this particular threat. It’s also a good idea to monitor logs for signs of exploitation attempts.

Read full article

Comments



Read the whole story
fxer
1 hour ago
reply
Bend, Oregon
Share this story
Delete

The Internet goes on high alert after discovery of 8 compromised TLS certs

1 Share

Security personnel around the world are on high alert Tuesday following the discovery of eight TLS certificates with private keys so weak they could allow anyone to mint trusted browser and app credentials for any site on the Internet.

As of late morning Tuesday, browser makers and some major apps and programming languages had blocked all eight of the intermediate certificates. There are no reports of certificate transparency logs, which track the issuance of all browser-trusted certificates, showing the compromised keys being used maliciously. The threat remains far from over, however, because it will be hard and time-consuming to update other key parts of the Internet, such as Linux distributions and embedded and Internet of Things devices.

One word: bonkers

The eight intermediate certificates belong to India-based certificate authority eMudhra Limited. An informal advisory published to emudhra.we-have-a-problem.com over on Tuesday posted the message “We have a problem here - Wayne.” The words were digitally signed using the private key of one of the eMudhra certificates. With proof that the reporting party had control of the key, defenders scrambled because the same key could be used to sign unauthorized certificates that would be trusted by millions of servers worldwide.

“This will be a massive cleanup job, bigger than Heartbleed,” Filippo Valsorda, a cryptography engineer and a cryptography maintainer for the open source Go programming language, told Ars. “There will be a very, very long tail, IoT devices, Docker containers, forgotten Linux machines, unmaintained CLI tools that shipped their own copy of the roots (which is common in some ecosystems, like Python). Also, Linux distributions are still rolling out updates, some of them are not ready yet, and then system administrators will need to apply them to a lot of machines.”

Heartbleed is the name of a critical vulnerability in the OpenSSL cryptography library. In 2014, it came under mass exploitation. Exploits let many unaffiliated hackers decrypt TLS-protected exchanges between parties. They also recovered private TLS certificate keys, session cookies, and passwords. The attacks compromised thousands of servers, some belonging to large companies and government agencies around the world.

Recovery required a long series of steps that took years. Steps included patching OpenSSL on all affected devices, reissuing millions of TLS keys, revoking old certificates, rotating passwords and session tokens and updating embedded devices and other forgotten systems—something that was extremely time- and resource-intensive, especially at Internet scale.

“Every time you need a lot of different people in different contexts to do something, it will take a long time,” Valsorda explained. “This time it’s worse because there’s more contexts, more people, and more heterogeneity.”

The compromised eMudhra keys were defective at a level that’s challenging the imagination of many of the engineers studying the incident. A normal size for a NIST P-384 elliptic curve cryptography private key contains roughly 384 bits of entropy, a size allowing almost 2384, or a number with 116 digits, different possibilities. The private key sizes of the compromised keys ranged from 3 to 8 bits. Astonishingly, the private keys were 4, 56, 66, 115, 155, 156, 230, 237.

“That is extremely in the ‘this should not be possible’ category,” Valdorda said. “Maybe some horribly dangerous key generation interface has a ‘size’ parameter and they set it to 1 by mistake???”

Ben Cartwright-Cox, director of BGP.tools, said: “My guess is that it's example code that accidentally leaked to production, but hard to know. But it’s bonkers that no one noticed.”

At this early stage, the most immediate threat appears to be for those using VPNs, especially in countries with governments likely to maliciously intercept traffic. There are likely many other cases for concern. End users largely have no recourse other than to hold off using many non-browser forms of TLS communication until they receive assurances updates are in place.

As noted, most browsers have already blocked the intermediate certificates. The exception appears to be Edge running on Windows 10, which at the time this article went live was still connecting to 12 vulnerable hosts. In response to questions asking why and if the company has plans to do so, a Microsoft representative the company will be in touch if it has anything to "share." Meanwhile, Signal, WhatsApp, Wireguard, and other apps that don’t rely on TLS for confidentiality aren’t affected. This page and the emudhra.we-have-a-problem.com site show apps known to be patched so far.

The incident is the latest to expose a fatal flaw in the TLS regimen. It's only as strong as its weakest link, which in this case was eMudhra. Fortunately, transparency logs account for much of that failure, but this measure requires parties to actively monitor massive feeds and works only after unauthorized certificates have been issued. eMudhra representatives weren't immediately available to answer questions.

One caveat: exploiting compromised certificates requires an active adversary-in-the-middle attack, meaning the attacker must act as a proxy between two TLS parties and receive encrypted traffic, decrypt it, reencrypt it, and send it to the other party. Such capabilities, in some cases, are usually limited to only the most well-resourced attackers. People with control of a local network—at a coffee shop, university, or other organization—face much less of a challenge.

Read full article

Comments


Read the whole story
fxer
6 days ago
reply
Bend, Oregon
Share this story
Delete

PHP maintainers tell Web devs to prepare themselves for critical security patches

1 Comment

Website admins, brace yourselves. Fixes for what are believed to be uncommonly severe vulnerabilities are scheduled to drop in a little more than 12 hours for PHP, a programming language that powers websites and Web applications everywhere.

PHP maintainers said Monday that they planned to release patches for two vulnerabilities, both with severity ratings of 9.2 out of a possible 10.

Waiting for PHP2Shell

“All PHP users are encouraged to prepare now so they can upgrade as soon as the release is available,” the advisory stated. “We reserve the right to release earlier should details of either vulnerability become public, or should evidence of active exploitation appear in the wild.”

The maintainers published the advisory following the leaking of purported details, which have yet to be confirmed. The report showed a video of an exploit tool dubbed PHP2Shell executing code on webservers running WordPress 7.1.3, MediaWiki 1.46.2, phpBB 3.3.17, Magento 2.4.9, Joomla 6.2.0, Laravel 13.36.0, Laravel 8.83.29, Symphony 8.1.9, Drupal 11.4.10, and WHMCS 9.0.9, all of which use PHP. A video depicting the tool has been reposted here.

Attempts to locate the unconfirmed report were unsuccessful, but security firm watchTowr said it claimed to affect every PHP version from PHP 5, released in 2004, onward. The security firm went on to say it has confirmed that the vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, are real.

Researchers from separate security firm Sansec said they “expect mass attacks to start within 15 minutes of the release.” A third security firm, Webfence, also urged admins to prepare now. Huntress has also issued an advisory.

Preparation steps include identifying who is responsible for managing PHP inside an organization, taking an inventory of every app built on the language, planning a maintenance window starting at 14:00 UTC with contingency plans for earlier, making a backup of site and database files, and monitoring the PHP.net homepage for any late-breaking announcements, including an earlier release time. Some experts suggest unplugging any non-essential systems until they're patched.

As an open-source scripting language for building dynamic websites and web apps, PHP has come to be a de facto building block for the Web. It runs multiple CMS apps in addition to WordPress and also powers many internal tools. One security researcher said an estimated 1.3 million Internet-connected hosts are likely affected. Vulnerabilities with the severity the advisories are describing have the potential to inflict major damage across the Internet. Admins should remain aware that the patches can be released at any moment and remain vigilant until they do.

Read full article

Comments


Read the whole story
fxer
7 days ago
reply
Just have that repost on a daily timer
Bend, Oregon
Share this story
Delete

Review: 4-hour Musk documentary feels like two different films

1 Share

Elon Musk is a very familiar figure to Ars readers, given his massive influence (for better and worse) on the technology sector over the last 20 years. Oscar-winning director Alex Gibney's latest biographical documentary—simply titled Musk—covers a lot of well-known ground and challenges the carefully crafted public image of Musk as a visionary tech titan.

Gibney's documentary presents Musk as more of a Gilded Age confidence man, rejiggered for the 21st century: an investor cosplaying as an inventor whose real genius is pumping stocks and dazzling investors and the public alike with visions of a high-tech utopian future. The film is bound to push all the right outrage buttons, whether one is a Musk fan or a detractor—which makes it very much a product of the peculiar social media-driven era in which we live.

Gibney has been making documentaries since the 1980s, covering such varied subjects as Jimi Hendrix, Hunter S. Thompson and gonzo journalism, WikiLeaks, Scientology, Steve Jobs, Elizabeth Holmes (the subject of another forthcoming documentary, You Can See Everything, featuring comedian Nathan Fielder), Boris Becker, The Sopranos creator David Chase, alleged Russian interference in the US 2016 presidential election, the opioid epidemic, and cyclist Lance Armstrong. He snagged his first Oscar nomination for 2005’s Enron: The Smartest Guys in the Room, and won the Oscar for Best Documentary Feature two years later for Taxi to the Dark Side.

Tackling the subject of Elon Musk seems like a natural progression from those earlier works. Gibney has never been one to shy away from controversy, but even before Musk's release, the film drew the ire of its subject and threats of a defamation lawsuit. There were even (as yet unfounded) rumors that Universal Pictures was getting cold feet about theatrically releasing the film in international markets.

There's certainly no shortage of material for Gibney to work with and the film covers the most well-known aspects of Musk's life: Tesla and the fatalities linked to its driver-assistance systems, SpaceX, Starlink, his purchase of Twitter, his shift from warning about the risks of AI to fully embracing it with Grok, his embrace of Trump, the creation of DOGE, his alleged drug use, and his 14 (possibly more) children. Those interviewed include ex-wife Justine Musk, Kara Swisher, Martin Eberhard, Geoffrey Hinton, former MAGA influencer Ashley St. Clair (who bore a child by Musk), Cory Doctorow, Adam Becker, and Sam Harris. David Byrne co-wrote and performed an original song for the soundtrack, “Let Me Sell You a Dream,” incorporating more of Musk’s words.

Gibney is a gifted filmmaker and Musk is exceptionally well-done. But the documentary ends up feeling like two very different films. The first half focuses on the early entrepreneurial years, deftly incorporating archival footage with the usual talking heads. It reminds us of who Musk used to be—honestly, I miss that public version of Musk, even if it was carefully cultivated—and what little is known about his family background serves to humanize him a little.

Visionary or flim-flam man?

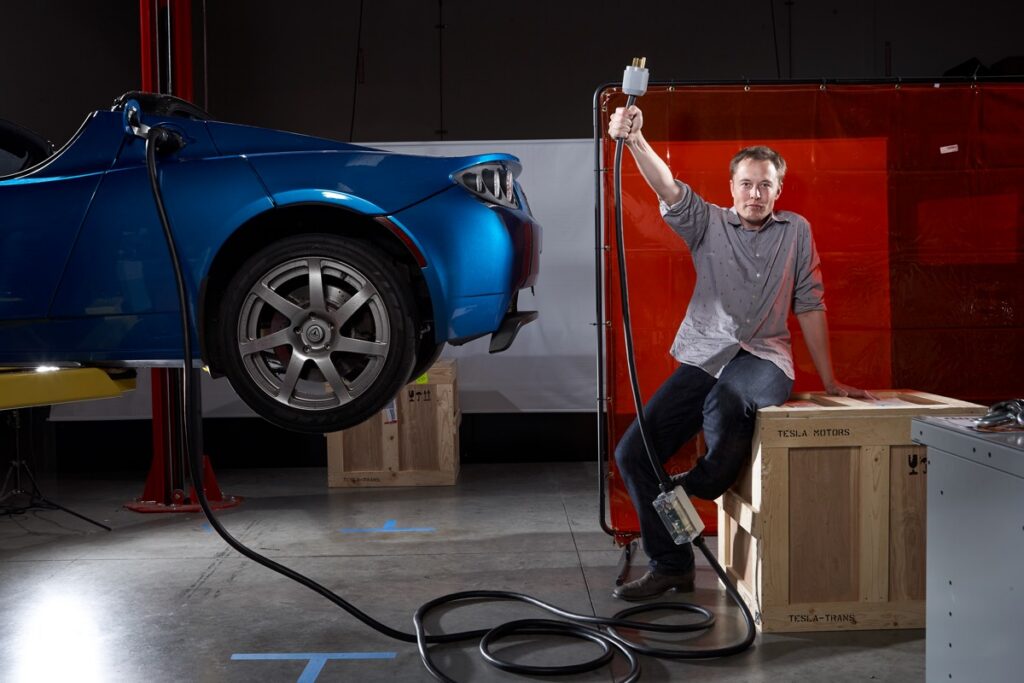
young Elon Musk sitting on a wooden crate while brandishing a charger in one raised hand. A blue early Tesla prototype is to the left.
Musk then Credit: Greg Segal
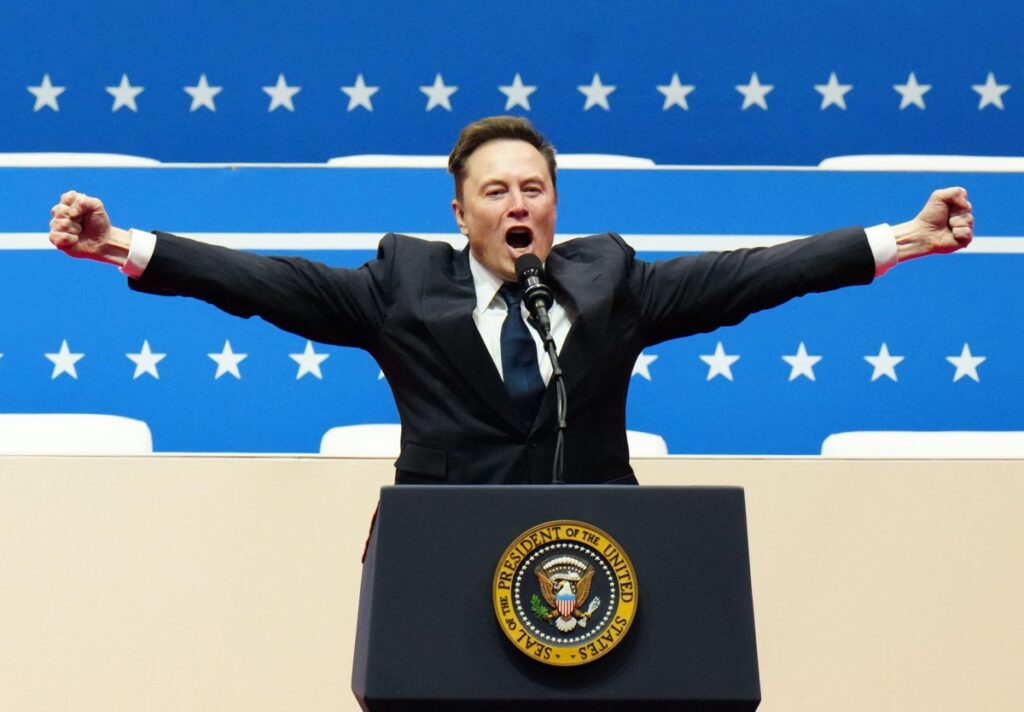
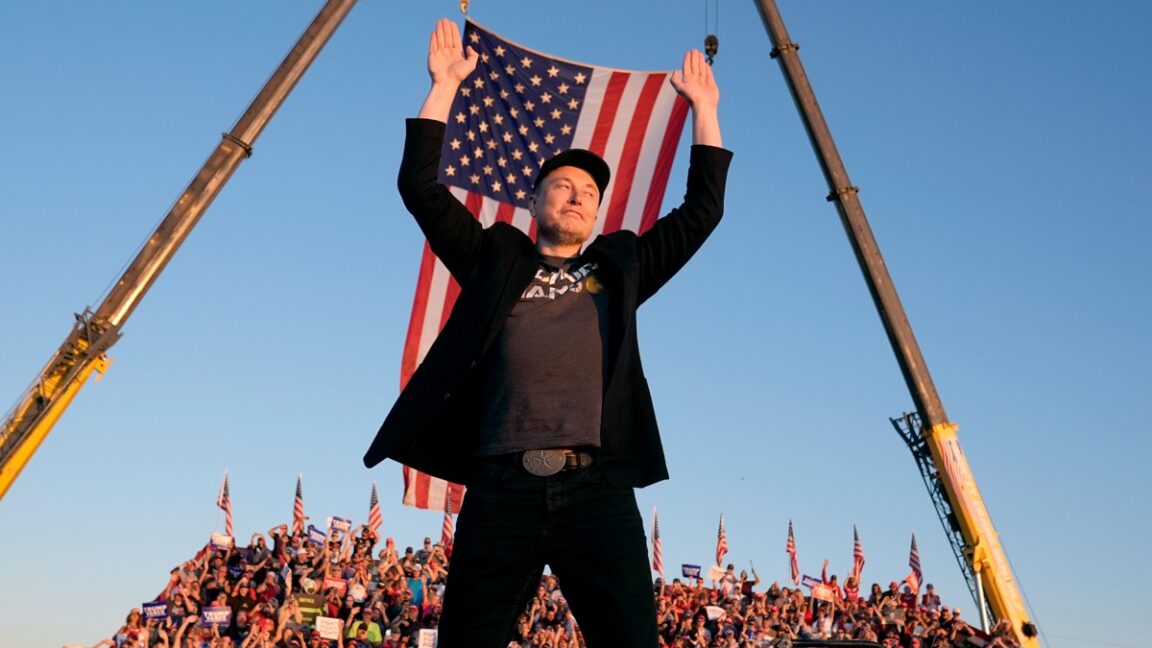
Older Musk in dark blue suit and tie, standing at podium at political event, arms spread wide, as he speaks into a microphone
Musk now. Credit: Ken Cedenoupi/UPI Alamy

The second half focuses on Musk after his purchase of Twitter and embrace of Trump. The notoriously thin-skinned Musk has accused Gibney of making a "hit piece." It's not, but the tone in the second half is markedly different and certainly more adversarial, leaving little doubt as to where Gibney stands. (The director is a staunch critic of the so-called journalistic "view from nowhere" and his documentaries typically have a strong point of view.)

During a post-screening Q&A, Gibney revealed that he'd actually finished the documentary in 2024, but HBO asked him to keep going to document Musk's "heel turn," if you will. One assumes he recut the first half in the process, but perhaps that's why Musk feels like two different documentary films smushed together. It's also how the documentary ballooned to a nearly four-hour run time (with a 10-minute intermission). Gibney joked during the Q&A that the real question should be, how did he limit himself to just four hours when it could easily been stretched to six? In that case, perhaps it might have worked better as a six-episode documentary miniseries.

Musk declined to be interviewed for the film, so the director created an AI version of Musk uttering verbatim public quotes as a stand-in for a real interview. I get why Gibney decided to do this and it's conceptually apt: this is the AI future that Musk and his ilk are working so hard to bring about, popular opinion be damned. So sure, give him the AI avatar treatment. But the execution is lacking; it's creepy uncanny valley stuff. The AI Musk pales in comparison with the archival footage of the actual Musk, which is far more interesting precisely because it's real.

Musk is a frequently compelling portrait of a complicated man but that portrait is incomplete in some crucial ways. Gibney's portrayal is as much tragic anti-hero as con artist or flim-flam man—an idealistic dreamer ultimately corrupted by wealth and power, or what Gibney calls "noble cause corruption." The first half of the documentary made me mourn who Musk once was, and wonder what kind of man he might have become had he made different choices at crucial points on his rise to the top. But the film sheds little light on why he ended up on such a dark path.

Would Musk agreeing to be interviewed have helped? I am not so sure. This is a man, as the film makes clear, who really isn't capable of self-reflection or facing hard truths, and he has the wherewithal to keep his bubble intact. As his wealth and influence have increased, so has his detachment from reality. Somehow it still hasn't made him happy.

Musk is now playing in select theaters in New York and Los Angeles. It will open broadly across the US on October 14, 2026.

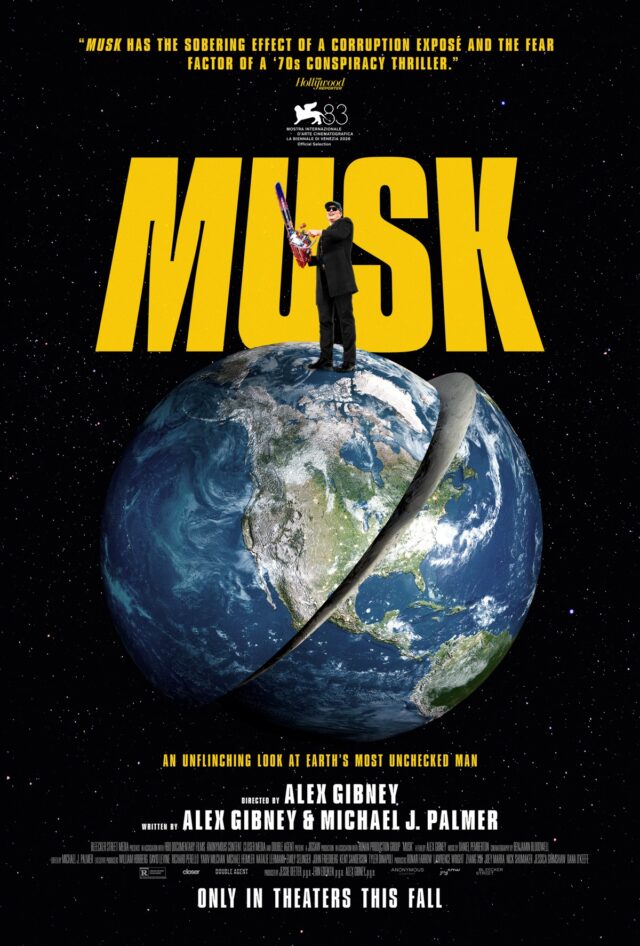
poster art for Musk documentary showing the planet earth with Musk standing on top wielding a chain saw Credit: Bleecker Street


Read full article

Comments


Read the whole story
fxer
16 days ago
reply
Bend, Oregon
Share this story
Delete

Prime Video unveils Blade Runner 2099 full trailer at NYCC

1 Share

We got our first look at Prime Video's new sci-fi series Blade Runner 2099 in July at San Diego Comic-Con. With the show's premiere roughly six weeks away, the streamer unveiled the full trailer this weekend at New York Comic-Con. Co-stars Michelle Yeoh and Hunter Schafer (Euphoria) joined showrunner Silka Luisa (Shining Girls) onstage for the big reveal.

As Luisa described the show during the NYCC panel Saturday night:

We are 50 years after [Blade Runner] 2049 and, bad news, the worst has happened. The replicant uprising that has been bubbling up in the films has taken place and the humans have lost. So the creations have surpassed their creators. And the series, the big question it asks is, ‘What happens when our time as a species ends?’ 2099 is taking place at a junction point when one species is ending and a new one is rising. The first film, something I loved about it, was that it was looking at mortality on a micro level. Roy Batty and the other replicants were fighting for more life. This show asks that same question but on a macro level. Mankind—what happens when we realize our time is running out? And are we going to accept that loss? Can we hold on to our humanity during it?

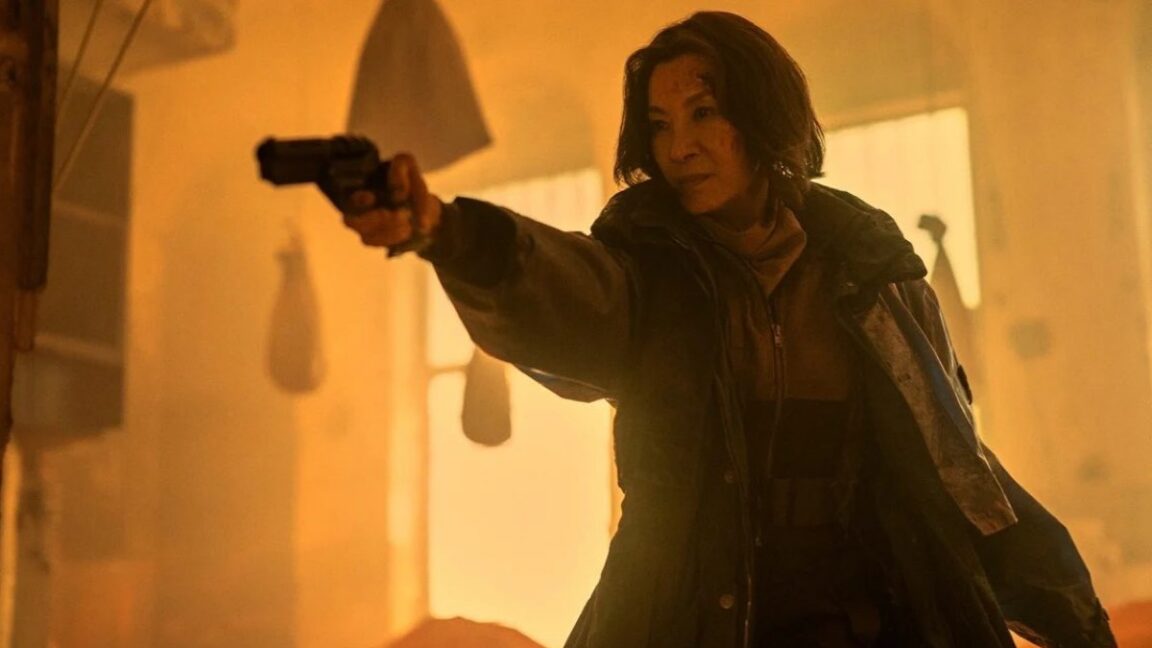
Yeoh stars as Olwen, the dying Replicant, while Schafer plays Cora. The cast also includes Hugo Hamlet as Buster Friendly, as well as Dmitri Abold, Lewis Gribben, Katelyn Rose Downey, Daniel Rigby, Johnny Harris, Amy Lennox, Sheila Atim, Matthew Needham, Tom Burke, and Maurizio Lombardi—all in as-yet-undisclosed roles.

Prime Video will drop all eight episodes of Blade Runner 2099 on November 25, 2026.

Godzilla Minus Zero

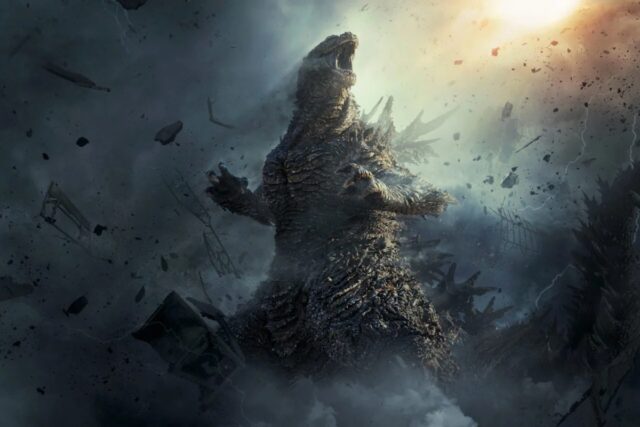
We also got a new trailer for Godzilla Minus Zero, the sequel to director Takashi Yamazaki’s gloriously grounded kaiju epic, Godzilla Minus One, which became a major international hit and snagged an Oscar for best visual effects.

Godzilla Minus One focused on kamikaze pilot Kōichi Shikishima, who struggled with survivor’s guilt after he failed to take action when Godzilla attacked the Japanese base on Odo Island in 1945. Kōichi was one of only two survivors and rebuilt a life with a woman named Noriko and the orphaned baby she rescued, Akiko. But then Godzilla re-emerged, and Kōichi resolved to die fighting the monster to atone for Odo Island.

Credit: Toho International

Spoiler alert: Kōichi survived, thanks to Tachibana’s forgiveness and mechanical ingenuity. He reunited with Noriko, who had a strange black bruise on her neck. And we saw a chunk of Godzilla’s remains start to regenerate, leaving things open for the sequel. Per the official synopsis for Godzilla Minus Zero:

War reduced Japan to zero, and Godzilla plunged it into minus. Two years have passed since then, and the country has faced agonizing struggles to achieve recovery and finally reclaim its daily life. Just as humanity managed to cling to a hard-won peace, a new threat strikes, crushing hope in an instant. There is no third time. Everything ends here.

Most of the main cast from Godzilla Minus One are returning: Ryunosuke Kamiki as Kōichi; Minami Hamabe as his wife, Noriko; Sae Nagatani as Akiko; Hidetaka Yoshioka as Kenji Noda, director of the Large-Scale Disaster Response Bureau; Kuranosuke Sasaki as Seiji Akitsu, captain of the Shinsei Maru; Miou Tanaka as Tatsuo Hotta, former captain of the destroyer Yukikaze; Sakura Ando as Sumiko Ōta, Kōichi’s neighbor; and Yuki Yamada as Shirō Mizushima, a Shinsei Maru crewman. The cast also includes Min Tanaka as biologist Kanji Murakami and Masami Nagasawa as Aoyama.

Godzilla Minus Zero hits theaters on November 3, 2026. Legendary Pictures plans to release Godzilla x Kong: Supernova—its Monsterverse sequel to 2024’s Godzilla x Kong: The New Empire—in 2027.


Read full article

Comments


Read the whole story
fxer
16 days ago
reply
Bend, Oregon
Share this story
Delete
Next Page of Stories